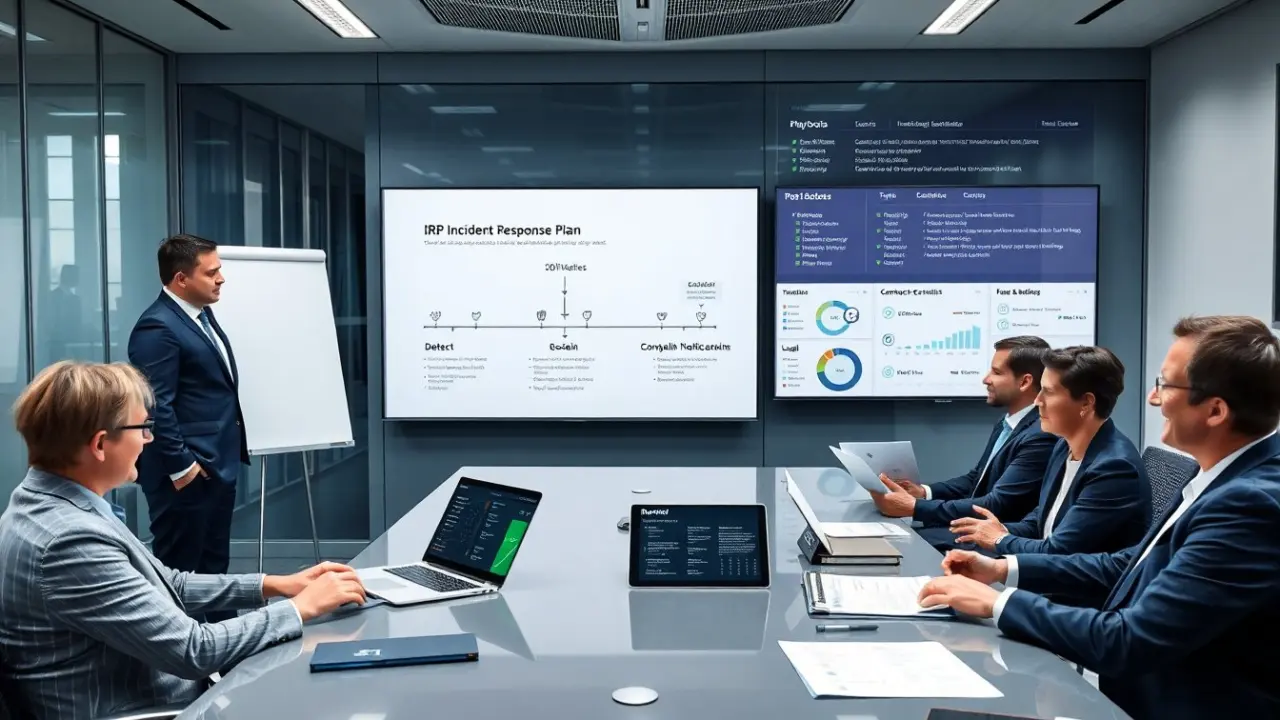
An irp incident response plan sets clear steps for detecting, containing, and recovering from security incidents. It assigns roles, defines communication paths, and lists tools for response. Organizations use an irp incident response plan to lower damage, reduce downtime, and meet compliance. This article explains why the irp incident response plan matters and how to build one.
Key Takeaways
- An irp incident response plan provides clear, step-by-step guidance for detecting, containing, and recovering from security incidents to minimize damage and downtime.
- Assigning specific roles and responsibilities in the irp incident response plan ensures coordinated actions and effective communication during an incident.
- Develop and regularly update playbooks tailored to common incidents that include evidence collection, containment, and recovery procedures.
- Test your irp incident response plan frequently through tabletop exercises and technical simulations to identify gaps and improve response times.
- Maintain compliance by incorporating legal, privacy, and regulatory requirements into the irp incident response plan, including notification templates and timelines.
- Track key metrics like time to detect, contain, and recover to measure effectiveness and continually refine the irp incident response plan.
Why An Incident Response Plan (IRP) Is Essential For Every Organization
An irp incident response plan gives teams a clear path when incidents occur. It reduces confusion and speeds decision making. Leaders who have an irp incident response plan can limit data loss and avoid long outages. Regulators and customers expect documented processes. An irp incident response plan helps prove that an organization meets legal and contractual duties. Insurance carriers often require an irp incident response plan to qualify for cyber coverage. Small teams that lack a formal irp incident response plan often react ad hoc. Ad hoc reactions create inconsistent outcomes and increase cost. Large teams that use an irp incident response plan coordinate across departments. They run repeatable steps for containment and recovery. The plan also supports communication with executives, legal, and regulators. This support lowers reputational damage. An irp incident response plan also sets metrics. Teams can track time to detect, time to contain, and time to recover. These metrics show whether the plan works and where to improve. In short, an irp incident response plan turns crisis into process.
Core Components Of An Effective IRP: Roles, Playbooks, And Tools
An irp incident response plan must name roles and responsibilities. It must say who declares an incident, who leads containment, and who handles external messages. The plan must list contact details and escalation paths. An irp incident response plan must include playbooks for common scenarios. Playbooks give stepwise actions for malware, data breach, insider threat, and denial of service. Each playbook must state evidence collection steps and preservation methods. The playbooks must also list quick containment measures and recovery steps. The irp incident response plan must map tools to tasks. Teams should link logging and alerting tools to detection playbooks. They should link forensic tools to evidence collection. They should link backup and restore tools to recovery playbooks. The plan must include a communication template. Templates should cover internal updates, regulator notices, and customer messaging. The plan must include legal and privacy checks. Legal must approve any external statement before release. The plan should include vendor and third‑party contact steps. It should say when to bring in external forensics. The plan must keep an inventory of critical assets and data flows. That inventory helps prioritize response efforts. Finally, the plan must list metrics and reporting cadence. Teams should run post-incident reviews and update the plan after each incident.
How To Build, Test, And Maintain Your IRP — A Step‑By‑Step Approach
Start with scope and policy. A team should define what types of incidents the irp incident response plan covers. The team should set goals and success metrics. Second, assign roles. The team should name an incident commander, technical leads, communications lead, and legal lead. Third, create playbooks for the top risks. The team should prioritize playbooks by likelihood and impact. Fourth, map tools and data. The team should ensure logs, alerts, and backups feed into the plan. Fifth, run tabletop exercises. Tabletop exercises test decisions and communications. They reveal gaps in roles and timing. Sixth, run technical simulations. Simulations test detection, containment, and recovery steps on real systems in a safe environment. Seventh, document after actions. The team should capture lessons, assign fixes, and set deadlines. Eighth, update the irp incident response plan on a regular schedule. Teams should revise the plan after each test and after major system changes. Ninth, train staff and new hires on the irp incident response plan. Short drills keep muscle memory active. Tenth, measure and report. The team should track detection time, containment time, and recovery time. The team should report metrics to leadership and adjust the plan if metrics fail targets. This stepwise approach helps teams build a usable irp incident response plan and keep it current.
Common Pitfalls, Compliance Considerations, And Best Practices For IRPs
A common pitfall is a plan that sits unused. Teams must test the irp incident response plan often. Another pitfall is unclear ownership. The plan must name an owner who drives updates. Relying on a single tool is a risk. The plan should include alternative methods for detection and recovery. Teams often forget legal and privacy steps. The plan should include template notifications that meet local laws. Teams must check breach notification timelines and data breach thresholds. For compliance, organizations should map the irp incident response plan to applicable standards. Those standards include GDPR, HIPAA, PCI DSS, and sector rules. Auditors look for documented roles, tests, and evidence of fixes. For best practice, keep playbooks short and action focused. Use checklists that staff can follow under pressure. Automate containment where safe. Use runbooks that link to scripts and orchestration tools. Keep contact lists current and store them in multiple locations. Run joint exercises with vendors and partners. Capture metrics and use them to prove improvement. Finally, treat the irp incident response plan as living policy. Teams should update it after every test, incident, or infrastructure change.