The vendor risk management process must start with a clear goal. It must protect data, operations, and reputation. The process must assign roles, set risk appetite, and map vendors. The team must measure vendor performance and update controls. This article explains a practical vendor risk management process that teams can adopt in 2026.
Key Takeaways
- The vendor risk management process starts by defining scope, roles, and risk appetite to protect data and operations effectively.
- Maintaining an up-to-date vendor inventory with detailed categorization enhances risk visibility and accountability.
- Due diligence before onboarding includes verifying security, financial stability, and contract safeguards to mitigate risks.
- Continuous monitoring and incident response plans involving vendors are essential for timely risk detection and recovery.
- Regular performance measurement and control updates ensure the vendor risk management process adapts to evolving threats and compliance needs.
Why Vendor Risk Management Matters Today
Organizations rely on external providers. They share data, access systems, and run services. A vendor risk management process helps leaders see risks before they harm operations. It reduces breaches, outages, and compliance failures. It also reduces legal and financial exposure. Regulators now expect documented vendor risk management process steps. Boards ask for evidence of control over third-party relationships. Teams that apply a consistent vendor risk management process cut response time and lower remediation costs.
Beyond compliance, mature vendor risk management enables better business decisions: whether to insource, negotiate stronger SLAs, or diversify suppliers to reduce concentration risk. It brings procurement, legal, security, and business units onto a single framework so that vendor decisions reflect operational requirements and risk tolerance. A robust process also supports audits, mergers and acquisitions, and continuity planning by providing clear records of vendor risk posture over time.
Define Scope, Roles, And Risk Appetite
An organization must define the scope of the vendor risk management process first. It must list which services and data fall under review. It must assign ownership for vendor intake, assessment, and monitoring. The risk committee or senior leader must approve the risk appetite for vendors. The policy must state thresholds for high, medium, and low risk. The vendor risk management process must include approval gates and escalation paths. It must set review frequencies and reporting requirements for leadership.
Practical steps to implement this part of the vendor risk management process include: develop a written policy that identifies covered vendor types (e.g., cloud providers, payment processors, analytics vendors), map the data flows and access levels that increase risk, and define who can approve contracts at each risk tier. Establish clear role descriptions — for example, vendor owner (business), risk assessor (security/compliance), and contract approver (legal) — and embed the process into procurement checklists so assessments occur before purchase commitments.
Vendor Inventory And Categorization
The team must build a vendor inventory as the next step in the vendor risk management process. The inventory must include vendor name, service, contract dates, data access, and criticality. The list must stay current with automated feeds or regular updates. The organization must tag vendors by function, geography, and compliance needs. The vendor risk management process must link each vendor to a business owner and to technical contacts. This link helps when an incident affects a specific service.
When creating and maintaining the inventory, include fields that enable risk scoring and lifecycle management: contract renewal dates, subcontractors, logical and physical access, encryption and backup practices, insurance limits, and historic incidents. Use automation where possible — integrate procurement, ticketing, and cloud management tools to reduce stale records. Categorization should be practical: critical, important, and noncritical; and by risk domain (cybersecurity, privacy, financial, operational). This structured metadata enables filtering and prioritization for assessments and monitoring.
Due Diligence And Onboarding Controls
The vendor risk management process must require due diligence before onboarding. The team must request security questionnaires, audit reports, and certifications. They must check financial statements and legal records for stability. Contracts must include security clauses, incident notification timelines, and termination rights. The vendor risk management process must set minimum control requirements for high-risk vendors. The organization must require remediation plans for gaps and verify fixes before granting production access. The team must record approvals and store documents centrally.
Operationalizing due diligence means using standard templates and questionnaires that map to the organization’s risk criteria, such as baseline controls, encryption requirements, and identity/access management expectations. For higher-risk vendors, require evidence from independent audits (e.g., SOC reports) or perform onsite assessments if warranted. Legal should build standard contract language into templates that cover data processing, subcontractor use, liability caps, and audit rights. Ensure the vendor risk management process includes a formal sign-off gate that blocks provisioning until contractual and technical controls are validated.
Ongoing Monitoring, Incident Response, And Continuous Improvement
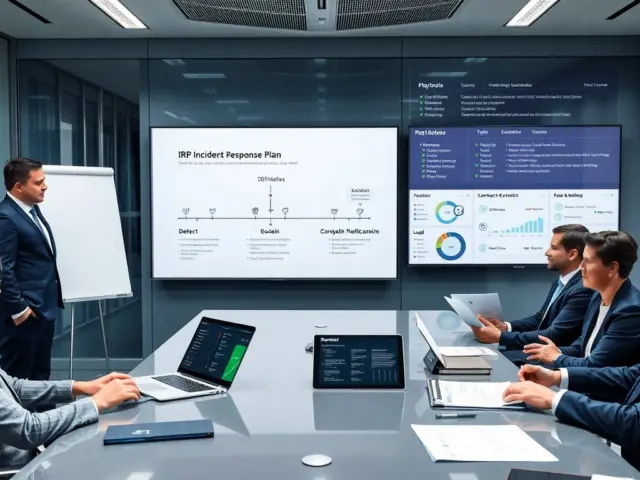
The vendor risk management process must include continuous monitoring after onboarding. The team must schedule periodic reassessments and require log access or reports for critical vendors. They must use alerts for configuration changes, new risks, or contract expiries. The incident response plan must include vendor roles, notification timelines, and recovery steps. The vendor risk management process must require tabletop exercises with key vendors for high-impact services. The organization must record lessons from incidents and update controls. The team must measure vendor performance with KPIs and adjust risk ratings based on evidence.
Concrete monitoring activities include automated security posture checks, vulnerability scanning where allowed, review of security event feeds, and quarterly control attestations from vendors. Track KPIs such as time-to-detect vendor incidents, time-to-remediate, SLA adherence, and number of open remediation items. Build escalation playbooks that spell out who notifies customers and regulators, who leads communications, and what data needs to be preserved. Post-incident, run root cause analysis that feeds back into the vendor risk management process: update questionnaires, change categorization rules, or require enhanced contractual safeguards when patterns emerge.
Finally, embed continuous improvement by running regular governance reviews, collecting metrics for leadership, and aligning vendor risk activities with enterprise risk management. Use the outputs to prioritize investments — for example, automation to reduce manual assessments, or enhanced training for vendor owners — so the vendor risk management process becomes more efficient and effective over time.