
what does cyber liability insurance cover is a common question for small business owners. The policy protects a business after a data breach, hack, or cyberattack. It covers response costs, liability to others, and some operational losses. This guide lists the main coverages, limits, and optional add‑ons. It helps a business owner compare policies and decide what fits their risk.
Key Takeaways
- Cyber liability insurance primarily covers costs related to data breaches, including breach response, forensic investigations, and business interruption losses.
- The policy provides third-party liability protection for lawsuits, regulatory penalties, and notification expenses arising from cyber incidents.
- Coverage limits, exclusions, and policy conditions like waiting periods and deductibles significantly impact the extent of protection a small business receives.
- Optional endorsements such as ransomware, social engineering, and PCI fines can expand coverage but require careful evaluation of costs and qualifications.
- Small businesses should verify critical policy terms including notification coverage, retroactive dates, and whether service providers are covered to ensure comprehensive protection.
- Utilizing insurer risk control services like incident response planning and employee training can help prevent cyber incidents and potentially reduce insurance premiums.
First-Party Coverage: Data Breach Response, Forensics, And Business Interruption
First-party coverage pays costs that the insured business incurs directly. Many policies pay for breach response. The insurer often covers legal counsel fees, public relations, and customer notification. The policy usually pays for credit monitoring for affected customers. Forensics costs get covered when the business wants to find the breach cause. The insurer often hires a forensic firm to trace the intrusion and preserve evidence.
Policies can cover business interruption losses that result from a cyber incident. The insurer may pay lost income and certain extra expenses while systems are offline. The policy sets a waiting period and a limit for these losses. Small businesses should verify the period of interruption covered. They should also check whether the policy covers dependent third‑party outages. Some policies include funds for system restoration and data recovery. The policy may pay for hardware replacement and software reinstallation. A business should confirm whether backups and cloud restorations get covered. The policy wording often limits payouts when the insured failed to follow basic security practices, so the business should review those conditions.
Third-Party Liability: Lawsuits, Regulatory Penalties, And Notification Costs
Third-party liability covers claims from customers, vendors, or partners. The insurer defends the business in lawsuits that allege data exposure or privacy failures. The policy often covers settlements and judgments up to the policy limit. It also covers legal fees and court costs.
Regulatory fines and penalties get addressed differently by each policy. Some policies pay regulatory defense costs but not all pay fines. A policy that covers regulatory fines will state that explicitly. The policy may cover costs for responding to government investigations and consent orders. Notification costs for affected individuals often fall under third-party coverage. The insurer may pay mailings, call center fees, and credit monitoring for affected people. The insurer may also pay for identity restoration services when identity theft follows a breach.
Small businesses should check whether the policy requires the insurer to preapprove settlement decisions. They should also verify the retroactive date and prior acts coverage. These items affect whether an old incident qualifies. The insured should confirm whether the policy covers claims from third parties outside the insured’s home country.
Common Exclusions And Coverage Limits To Watch
Policies often exclude intentional acts by the insured. Fraud by an owner or executive typically does not get covered. Many policies exclude bodily injury and property damage that arise from a cyber event unless the insurer lists those risks. War and nation‑state attacks may get excluded or limited. Some carriers exclude or limit coverage for attacks that the insured knew were likely and did not act on.
Coverage limits and sublimits can reduce payouts. An insurer may set a separate sublimit for regulatory fines, forensic costs, or notification expenses. Small businesses should compare aggregate limits and per‑claim limits. They should also watch for retention amounts and waiting periods for business interruption claims. Policies may require the insured to pay a deductible for each claim.
A business should confirm whether third‑party cloud providers and service vendors count as insureds or as third parties. The policy should state whether sublimits apply to claims that involve payment card data. The insured should also verify whether legal defense costs erode the limit available for settlements. These details change how much protection the policy gives in practice.
Typical Endorsements And Optional Add‑Ons (Ransomware, Social Engineering, PCI Fines)
Insurers offer endorsements that expand or clarify coverage. Ransomware coverage often pays ransom payments, negotiation costs, and extortion experts. Some insurers require proof of authorization and a clear chain of custody for ransom funds. Social engineering or fraud endorsements pay losses when employees are tricked into wiring funds or sending sensitive data. These endorsements often require documented training and controls to qualify.
PCI fines endorsements cover penalties from card brands for noncompliance with the Payment Card Industry standards. The insurer may pay investigation costs and fines up to a specified sublimit. Cyber crime endorsements can cover funds transfer fraud and forged payment instructions. The insurer may set strict conditions for proof and mitigation steps.
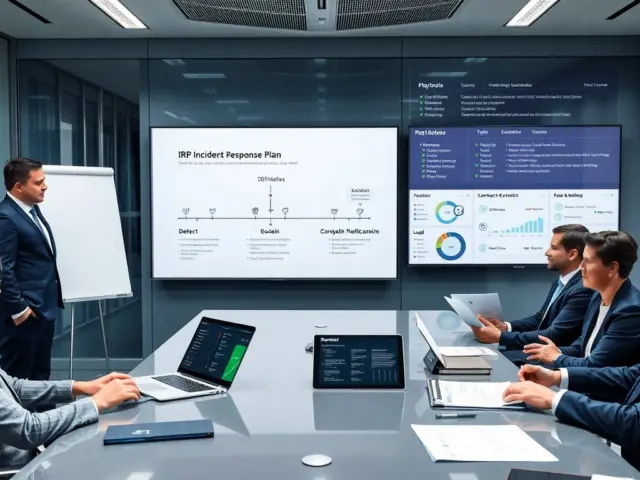
A business should weigh the cost of endorsements against likely exposure. It should request sample policy forms and read the endorsement wording carefully. The business should also ask about risk control services that carriers may offer, such as incident response planning, vendor assessments, and employee training. These services can reduce the chance of a payout and may lower premiums.